The Wallet Is Not the Safety Layer: How DeFi Users Should Think About dApp Integration
A common misconception in decentralized finance is that choosing a reputable wallet makes a transaction safe. It does not. A wallet can protect private keys, display warnings, and simulate a transaction, yet the final outcome still depends on the smart contract, the website, the assets involved, and the user’s approval decisions. The more accurate view is that a Web3 wallet is an interpretation and control layer between a person and an increasingly complex software system.
That distinction matters because DeFi transactions are not simple payments. When a user supplies liquidity, borrows against collateral, swaps tokens, or signs a message, the wallet is interacting with programmable contracts whose effects may be conditional, indirect, or difficult to reverse. A strong wallet cannot remove protocol risk. It can, however, reduce avoidable mistakes by helping the user understand what a dApp is requesting before a transaction reaches the blockchain.
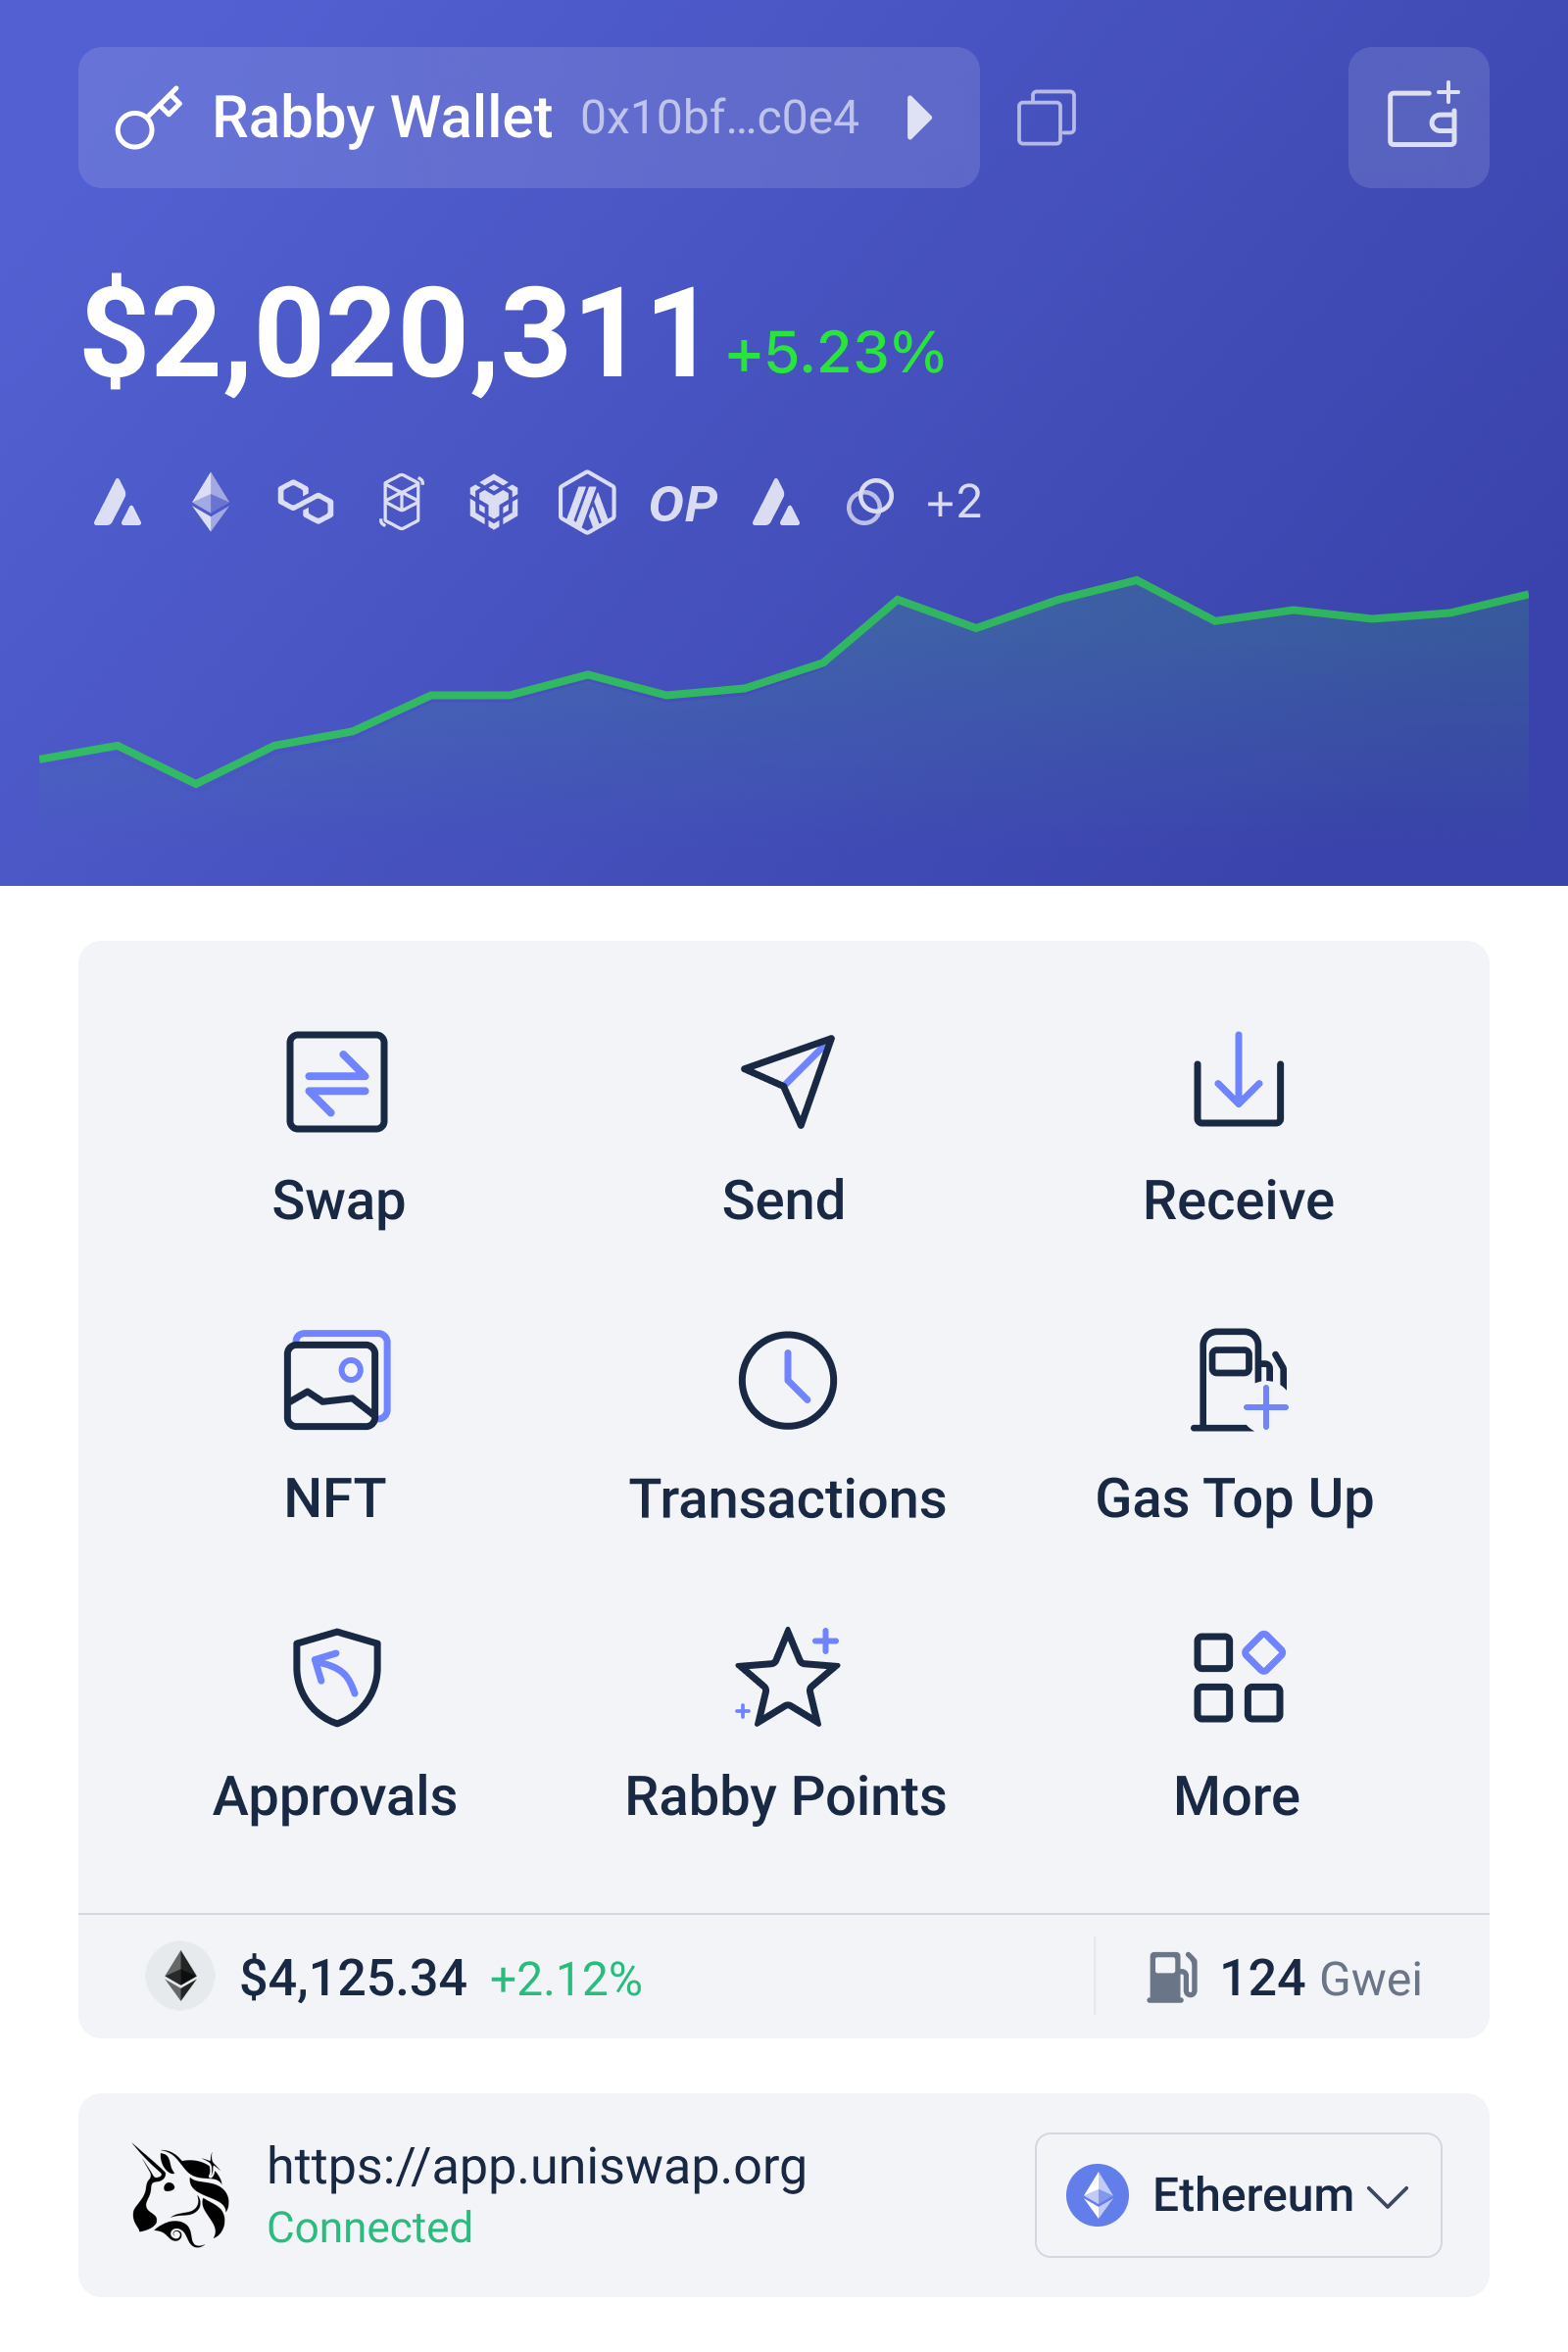
Myth: connecting a wallet means giving a dApp control of your funds
Connecting a wallet usually gives a decentralized application, or dApp, permission to view public blockchain information and request actions from the wallet. It does not automatically hand over the private key. The important boundary is between connection, signing, and token approval.
A connection lets a website know which address is active and which network the user is viewing. A signature authorizes a specific blockchain action or message. A token approval can authorize a smart contract to spend a defined asset on the user’s behalf, sometimes up to a very large limit. These are different events, but poorly designed interfaces can make them feel like one continuous click.
This is why wallet security is partly a problem of information design. Users do not merely need a confirmation button; they need a legible explanation of the proposed state change. A swap may involve a router contract, a token allowance, a minimum output amount, and a deadline. A lending transaction may alter collateral, debt, liquidation exposure, and interest-rate conditions. The visible action might say “Confirm,” while the economic consequences are much broader.
What transaction simulation can and cannot reveal
Transaction simulation attempts to execute a proposed transaction against a representation of the current blockchain state before the user signs it. In practical terms, it can help answer questions such as: Will the call revert? Which tokens are expected to leave the wallet? Which assets should arrive? Is an approval being created? Does the call appear to interact with the contract the user intended to use?
This is valuable because many failures are mechanical rather than mysterious. A simulation may expose an incorrect network, insufficient balance, an expired quote, an unexpected token transfer, or a contract call that does not match the user’s stated intention. For an active DeFi user, that preflight check is similar to reviewing an order ticket before submitting a trade.
But simulation is not proof of safety. It is a conditional preview. Its result depends on the state used for the simulation, the accuracy of the decoded contract data, and the assumption that the relevant environment will not change before the transaction is mined. DeFi markets can move between simulation and confirmation. A contract can contain logic that is difficult to model. A malicious site can present a familiar-looking explanation while requesting a different action. Some signatures, especially typed messages, may authorize future behavior without producing an immediate token transfer that is easy to visualize.
The sharper mental model is therefore not “simulation equals security.” It is “simulation reduces uncertainty about one proposed execution.” That reduction can be substantial, but it does not cover every risk category. It cannot independently establish that a protocol is solvent, that its oracle is sound, that its governance is trustworthy, or that the user’s computer and recovery phrase are uncompromised.
Why dApp integration creates a larger attack surface
DeFi users often focus on smart-contract exploits, yet the path to a loss can involve several layers. The wallet extension, browser, dApp front end, RPC provider, token contract, protocol contracts, and user approvals all form part of the operational environment. A weakness in any one layer may create confusion or an opportunity for abuse.
Front-end compromise is a particularly important boundary condition. A protocol may have audited contracts, but its website can still be redirected, altered, or imitated. The reverse is also possible: a polished website may route users toward contracts with dangerous permissions. Domain verification, network awareness, contract-address review, and wallet-generated warnings are not redundant tasks. They address different failure modes.
Chain selection adds another complication. Ethereum and EVM-compatible networks share broad technical conventions, but they do not share identical security assumptions, liquidity, bridge arrangements, or operational maturity. A token with the same symbol on two networks may represent different contracts and different risks. A transaction that is sensible on one chain may be meaningless or dangerous on another.
Recent messaging around Rabby Wallet has emphasized broad Ethereum and EVM coverage, with support intended to help users work across chains through Chrome and Brave. For users comparing an advanced rabby wallet experience with a basic signing tool, the meaningful question is not simply how many networks appear in a menu. It is whether the wallet makes chain context, contract intent, approvals, and likely outcomes easier to inspect before signing.
Myth: an audit or a warning makes a protocol safe
An audit is evidence about a particular codebase, scope, and point in time. It is not an insurance policy and does not establish that a protocol is economically robust. Audits can miss defects, interactions between contracts, governance failures, oracle problems, and risks introduced after the reviewed version.
Warnings have a similar limitation. A wallet may identify a suspicious address or an unusual approval, but a warning is a risk signal, not a final verdict. False positives are possible, and sophisticated attacks can resemble ordinary activity. Conversely, an absence of a warning does not mean that a protocol is suitable for a user’s risk tolerance.
This leads to a useful division of labor. The wallet should help with immediate transaction interpretation and operational hygiene. The user still needs to evaluate the protocol’s design, incentives, liquidity conditions, upgrade permissions, oracle dependencies, and exit paths. In the United States, where users may also face tax reporting and regulatory uncertainty, the wallet cannot determine whether a particular strategy is appropriate from a legal or financial-planning perspective.
A practical verification framework for DeFi transactions
Before signing, separate the decision into three questions: identity, intent, and consequence.
Identity asks whether the website, chain, contract, and token are the ones the user intended to use. Do not rely on a token symbol alone. Compare addresses through a trusted source, inspect the active network, and be cautious when a link arrives through an unsolicited message or social-media post.
Intent asks what the transaction is actually requesting. Is it a swap, an approval, a permit-style signature, a deposit, or an administrative action? Does the spender match the expected protocol? Is the requested allowance proportionate to the task? A user who cannot explain the transaction in plain language should usually pause rather than sign.
Consequence asks what changes if the transaction succeeds. Which assets leave the wallet? Which assets arrive? What risks are introduced by leverage, liquidation, lockups, impermanent loss, or variable rates? Could the position be unwound under stressed market conditions? Simulation is most useful here, but its output should be treated as a forecast of execution, not a guarantee of economic success.
Approval management deserves special attention. A high allowance can be convenient because it avoids repeated approval transactions, but convenience expands the potential damage if the spender contract is later exploited or if the user interacts with a malicious address. Smaller or task-specific approvals can reduce exposure, although they may cost more in fees and create additional transactions. This is a genuine trade-off, not a universal rule. The sensible choice depends on the asset’s value, the contract’s trust profile, and how frequently the user interacts with it.
The operational discipline that software cannot replace
Security features work best when paired with separation of roles. Many experienced users keep long-term holdings away from experimental DeFi activity and use a smaller operational wallet for routine interactions. A hardware signer can improve private-key protection, but it does not make a malicious transaction harmless; the signer may still approve it. Cold storage and transaction review solve different problems.
Users should also treat recovery phrases as the ultimate control mechanism. No dApp, support agent, or wallet representative needs that phrase to help with an ordinary transaction. A browser extension that is genuine today can still be installed on a compromised computer tomorrow. Device hygiene, phishing resistance, backups, and deliberate signing habits remain part of the security model.
One useful habit is to reduce transaction speed when transaction complexity rises. A familiar swap for a small amount may require a quick review. A new protocol, large approval, leveraged position, or unfamiliar signature deserves a slower process: verify the domain, inspect the contract, simulate the call, consider the worst plausible outcome, and only then sign. The goal is not to eliminate all risk. In open financial systems, that is unrealistic. The goal is to ensure that the risks taken are understood, bounded, and intentional.
What to watch as wallet tooling develops
If wallets continue improving their dApp integrations, the most useful progress will not be measured only by the number of supported chains. It will be measured by how clearly they translate machine-readable calls into economic meaning. Better decoding, clearer approval histories, more reliable simulations, and stronger separation between connection and signing could reduce the gap between what a contract requests and what a user thinks it requests.
The unresolved challenge is that DeFi risk is partly compositional. A wallet can inspect one transaction, while the real exposure may arise from several protocols, bridges, permissions, and market assumptions combined. Future tooling may provide better portfolio-level analysis, but users should remain skeptical of any interface that compresses complex risk into a single green badge.
Frequently asked questions
Does transaction simulation guarantee that a DeFi transaction is safe?
No. Simulation can reveal expected execution results, likely transfers, approvals, and reverts under a particular state. It cannot guarantee that the protocol is honest, that the market will remain stable, that the front end is authentic, or that the contract has no undiscovered vulnerability.
Should I revoke every token approval after using a dApp?
Not necessarily. Revoking approvals can reduce the damage from a compromised spender, but it costs an additional transaction and may be inconvenient for frequent users. Review approvals according to asset value, contract trust, exposure, and usage frequency rather than following an absolute rule.
What is the most important thing to check before signing?
Check that the transaction matches your intended action across three dimensions: the correct dApp and network, the expected contract and permissions, and the assets and economic consequences that will result. If any of those remain unclear, do not sign until the uncertainty is resolved.
A capable Web3 wallet is best understood as a risk-reduction instrument, not a substitute for judgment. Its strongest contribution is making hidden transaction mechanics more visible at the moment they matter. That can prevent costly mistakes, but the final security boundary remains the user’s decision to verify what is being authorized, why it is needed, and how much downside is acceptable.